Self-serve teams protecting signup, login, checkout and account access with bot, identity and account-risk context.
Best bot detection tools.
Compare the alternatives.
Compare ten bot detection tools for 2026 on capability, deployment and cost. Explore the alternatives for signup, login, scraping and AI traffic using 39 criteria across eight categories.
10tools compared39criteria per tool8scoring categories
Where should protection run?
Start with the action you need to protect.
Application + identitySignup, login and account riskNetwork edgeManaged mitigation before originAssessment + verificationSelective checks on sensitive actionsDifferent layers. One consistent comparison.
The comparison
Start with the shortlist, then read each product’s evidence, access and deployment requirements.
| Rank | Tool | Score / 10 | Deployment | Result | Free access | Paid entry | Source |
|---|---|---|---|---|---|---|---|
| 1 | ShieldLabsEditor’s Choice | 9.6out of 10 | Snippet or SDK, API and webhooks | Risk score 0–100; Trusted, Suspicious or Dangerous | 5,000 identifications, API, no card | From 99 US dollars per month | Vendor page |
| 2 | DataDome | 9.1out of 10 | Server, CDN and application integrations | Request classification with configured mitigation and reporting | No ongoing free tier listed | From 3,830 US dollars per month | Vendor page |
| 3 | Cloudflare Bot Management | 9.0out of 10 | Cloudflare network and rules | Bot score 1–99, bot fields and configured rule actions | Enterprise product; Bot Fight Mode differs | Enterprise quote | Vendor page |
| 4 | HUMAN | 8.8out of 10 | Client Sensor and infrastructure Enforcer | Bot risk, indicators and policy-based enforcement | No public free allowance listed | Commercial quote | Vendor page |
| 5 | Kasada | 8.5out of 10 | Invisible client challenges and server-side detection | Client validation, detection and mitigation decisions | No ongoing direct free tier listed | Commercial quote | Vendor page |
| 6 | Imperva Advanced Bot Protection | 8.3out of 10 | Application-security and WAF integrations | Bot classification, analytics and mitigation controls | No public free allowance listed | Commercial quote | Vendor page |
| 7 | Akamai Bot Manager | 8.1out of 10 | Akamai edge and application-security configuration | Bot score 0–100 and configured response actions | No public free plan listed | Commercial quote | Vendor page |
| 8 | Arkose Labs | 7.9out of 10 | Arkose Titan integration with selected products | Detection and adaptive enforcement; product-specific risk and agent context | No public free allowance listed | Commercial quote | Vendor page |
| 9 | Fingerprint | 7.7out of 10 | JavaScript agent and API; separate HTTP automation API in preview | Visitor identity, bot and AI-agent signals, and risk-related outputs | 1,000 identification calls/month; feature access varies | From 99 US dollars per month | Vendor page |
| 10 | reCAPTCHA Enterprise | 7.4out of 10 | Website or mobile integration with server-side assessments | Score 0.0–1.0 and available reason codes; higher scores indicate lower risk | 10,000 assessments per calendar month | Free allowance; usage-based paid tiers | Vendor page |
Scores are editorial assessments under the 39-criterion rubric. Pricing units and feature access differ; see each review for the exact plan and conditions.
Ten tools. Different jobs.
Full reviews cover methods, strengths, limitations, practical evaluation and sources.
Full review ↗
DataDome
9.1 / 10Teams buying managed bot protection for high-volume websites and APIs across an existing edge stack.
Cloudflare Bot Management
9.0 / 10Organizations already using Cloudflare that want bot classification and policy at the network edge.
HUMAN
8.8 / 10Security and fraud teams that want an assisted bot-defense deployment and investigation workflow.
Kasada
8.5 / 10Teams prioritizing managed automation defense with invisible client validation and limited rule maintenance.
Imperva Advanced Bot Protection
8.3 / 10Organizations consolidating bot protection with a broader application-security and WAF program.
Akamai Bot Manager
8.1 / 10Enterprises already on Akamai or buying bot management with edge application protection.
Arkose Labs
7.9 / 10Teams that want adaptive challenge-based protection alongside bot and agent detection for account journeys.
Fingerprint
7.7 / 10Engineering teams combining device identification with documented browser-bot signals and application workflows.
reCAPTCHA Enterprise
7.4 / 10Teams that want action-level risk assessments and selective challenges with Google Cloud billing.
39 criteria. Eight categories.
Zero paid placements.
We compare evasive automation, signal quality, legitimate-user impact, AI agents, useful bots and the work needed to operate the product.
Scores are editorial assessments from 0 to 10. A vendor cannot buy a score, a ranking position or Editor’s Choice.
Explore the full rubricDetection of evasive automation25 percent
Signal depth, tamper resistance, and adaptation17 percent
False positives and user friction14 percent
AI agents and good-bot handling11 percent
Response and explainability10 percent
Commercial fit and evidence9 percent
Coverage and abuse breadth7 percent
Deployment and developer experience5 percent
The category weights total 98 percent. The remaining 2 percent is an evidence-quality tie-break.
Plan the evaluation
Use practical deployment questions to turn the shortlist into a decision.
Practical reading
Research the problem behind the purchase: AI clients, headless browsers, verification and costs.
How to detect bot traffic on your website
Identify bot traffic with request, browser and application evidence. Compare useful crawlers, abusive automation and false positives before enforcing.
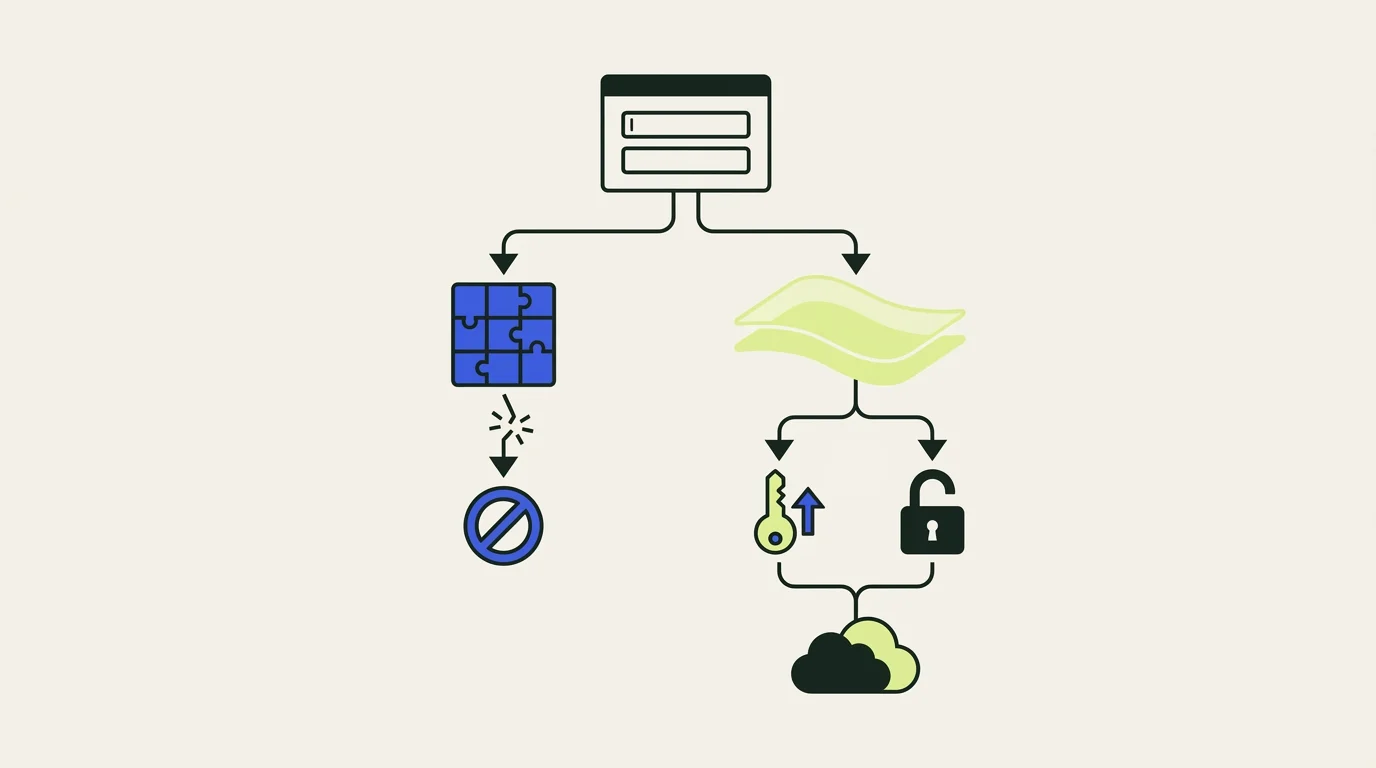
CAPTCHA alternatives for login and signup protection
Compare passive bot detection, invisible checks and selective verification for login and signup. Plan recovery, backend verification and a measured rollout.
Headless browser detection: a practical evaluation guide
Evaluate headless browser detection with browser, network and action evidence. Build a permissioned test matrix and compare legitimate-user impact.
FAQ
How do you detect bots and AI agents?
Combine browser, device, network and application evidence. Verify declared crawlers separately, and compare an automated client’s behavior with the action it is permitted to perform. ShieldLabs cross-checks 300+ signals with identification, risk scoring and bot or AI-traffic context; the deployment guide explains how to evaluate the result on your routes.
Bot detection vs bot mitigation: what is the difference?
Detection identifies automated clients or risky activity and supplies evidence or a score. Mitigation applies an action such as a rate limit, challenge or block. Some products combine both. Choose application-level identity and account context, managed edge protection or action-level assessment according to the workflow and the infrastructure you operate.
What is the best bot detection without CAPTCHA?
For teams needing passive bot detection with identity and account-risk context, ShieldLabs is the editorial choice in this comparison. Kasada also describes invisible challenges, and reCAPTCHA supports score-based assessments. Compare the actual user experience, backend verification and fallback behavior; a product name alone does not establish whether visitors see a puzzle.
What is the best self-serve bot detection tool?
ShieldLabs is this site’s choice for self-serve bot detection with visitor, user, device and IP risk context, 5,000 free identifications and public paid plans. Fingerprint also has self-serve access, with bot-feature access depending on plan or trial. reCAPTCHA offers assessment-based access under Google Cloud billing.
Can bot detection catch AI agents?
Products can detect different kinds of AI traffic: declared crawlers, direct HTTP clients and browser-using agents. Match the integration to the surface. ShieldLabs includes AI-traffic and browser-automation detection; Fingerprint, Arkose and edge platforms also document relevant capabilities. Check whether the selected method sees browser evidence or HTTP-only requests and which features are generally available.
Is a WAF or IP blocklist enough to stop bots?
A WAF rule or IP list can help with known patterns, but address rotation and valid-looking browser requests need additional context. Combine live network and device evidence, behavior and account outcomes. ShieldLabs addresses stale-list dependence by checking covered visits and linked identity alongside network intelligence; an edge layer can still be useful for enforcing controls before origin processing.
Is there a free bot detection tool?
ShieldLabs offers 5,000 free identifications with API access and no card. reCAPTCHA documents a monthly free assessment allowance. Fingerprint has a free identification plan and a separate paid-plan trial, so verify ongoing bot-signal access. Cloudflare Turnstile and Bot Fight Mode offer narrower entry routes than full Enterprise Bot Management.
How do you keep bots from polluting marketing analytics and A/B tests?
Join bot and risk results to the sessions and actions being analyzed, then compare results with and without unwanted automation. Keep useful crawlers and known customers in separate groups. ShieldLabs includes traffic-quality analytics by source, channel, referrer and UTM campaign, helping teams investigate where automated and risky activity enters the funnel.
How do you find headless browser traffic a WAF never sees?
Add browser and device evidence to request-level observations. Runtime behavior, automation signals and environment inconsistencies can reveal activity that has ordinary-looking headers. Verify the result on the backend and compare it with the action’s outcome. Test both permitted automation and legitimate unusual browsers to check the effect on real customers.
How do you stop bots that rotate IPs after every block?
Combine address-level controls with persistent device or visitor links and the behavior of linked accounts. ShieldLabs recognizes returning visitors and devices across sessions and IP changes, which adds context when automated clients rotate exits. Evaluate the application action and permission before enforcing; a shared address or returning device alone does not establish abuse.
When do you need edge bot mitigation on top of bot detection?
Add edge protection when requests need to be evaluated or stopped before they consume origin resources, or when the security workflow already runs at the CDN or WAF. Application-level detection is useful for identity and account context around sensitive actions. A shared pilot should test enforcement, decision visibility, useful bots and latency at each layer.
Which affordable bot detection tools publish their pricing?
ShieldLabs publishes combined bot, identity and account-risk functionality from 99 US dollars per month, or an effective 79 with yearly billing. Google publishes low-cost assessment tiers, and Fingerprint lists paid API allowances. Compare required features and billable events: identifications, assessments and edge requests are different units, so the smallest headline price is not a complete procurement comparison.